You can trace a fake email sender, but the email itself rarely names the person behind it. A header may show an IP address, and an IP address points to an internet provider and a general area. Getting from there to a name takes more: a subpoena to the email provider, a subpoena to the internet provider, or an investigation that connects the account to a real person through other evidence.
This guide covers each route to a fake email sender, what the header shows for Gmail, Outlook, Yahoo and Proton Mail, and when each route makes sense.
What tracing an email can tell you
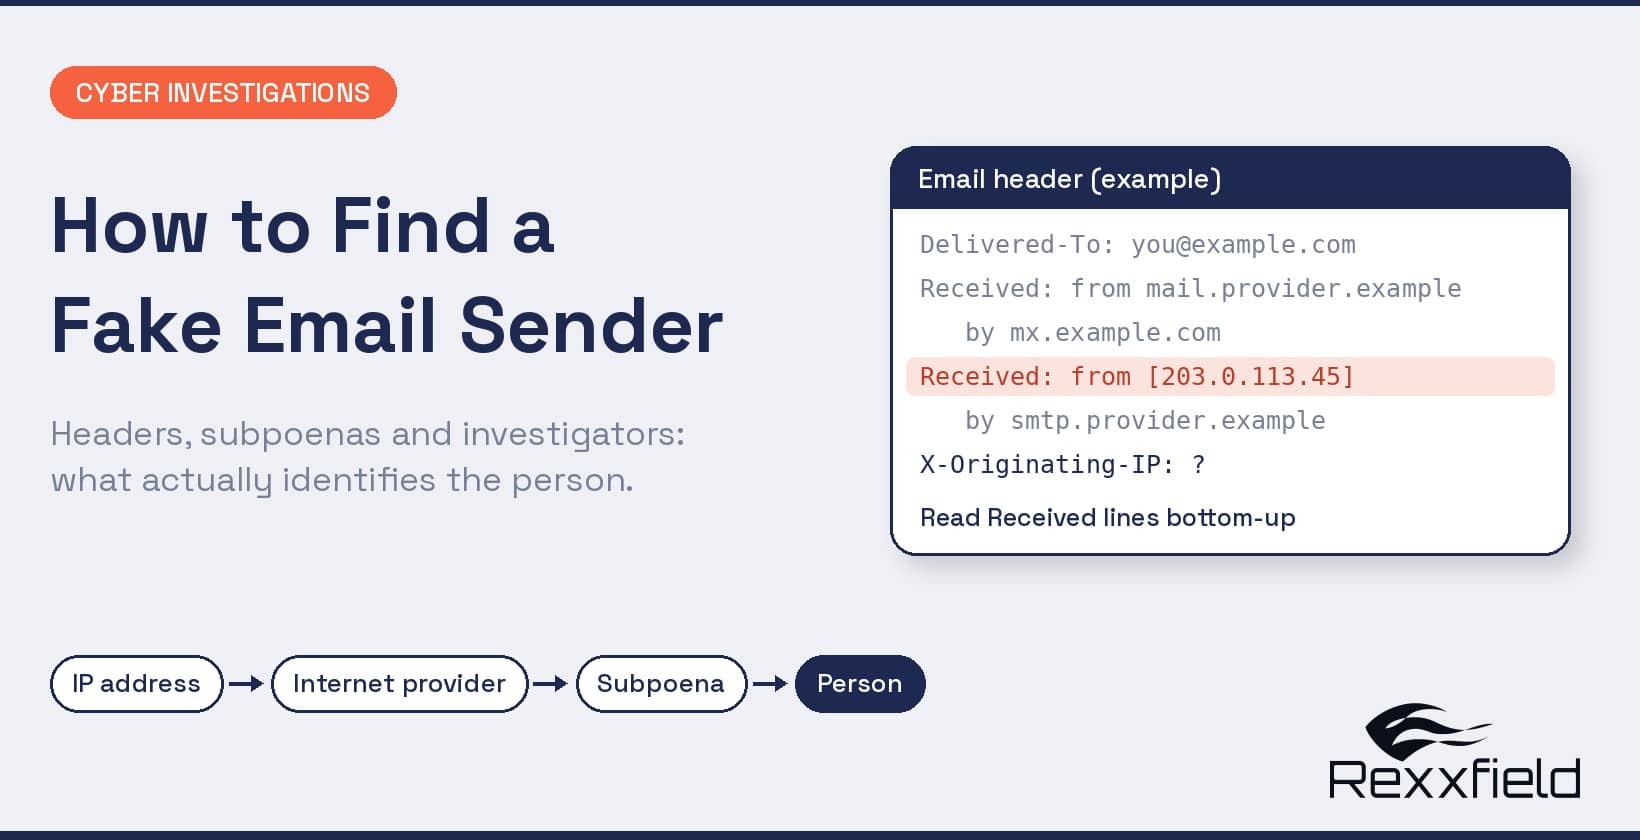
Tracing an email means finding the IP address of the device that sent it, then looking that address up. A lookup shows the internet service provider, the country, the region and usually the city. It does not show a street address, a name or a phone number. Only the provider that issued the address knows which customer used it at that moment, and it releases that record only in response to legal process.
Two things often make the result useless. The first is a VPN, proxy or Tor connection, which replaces the sender’s real address with the address of the service. Run any IP address you find through a VPN-detection tool such as VPNAPI.io before you draw conclusions from its location. The second is the email provider itself, which often replaces the sender’s address with its own. Our guide to what an IP address tells you explains what a lookup can and cannot show.
Step 1: Read the email header
Every email carries a header, a block of routing data that records each server the message passed through. To open it, use these paths:
- Gmail: open the message, click the three dots and select Show original.
- Outlook: open the message in its own window, click the three dots and select View, then View message source.
- Yahoo Mail: open the More actions menu and select View full headers.
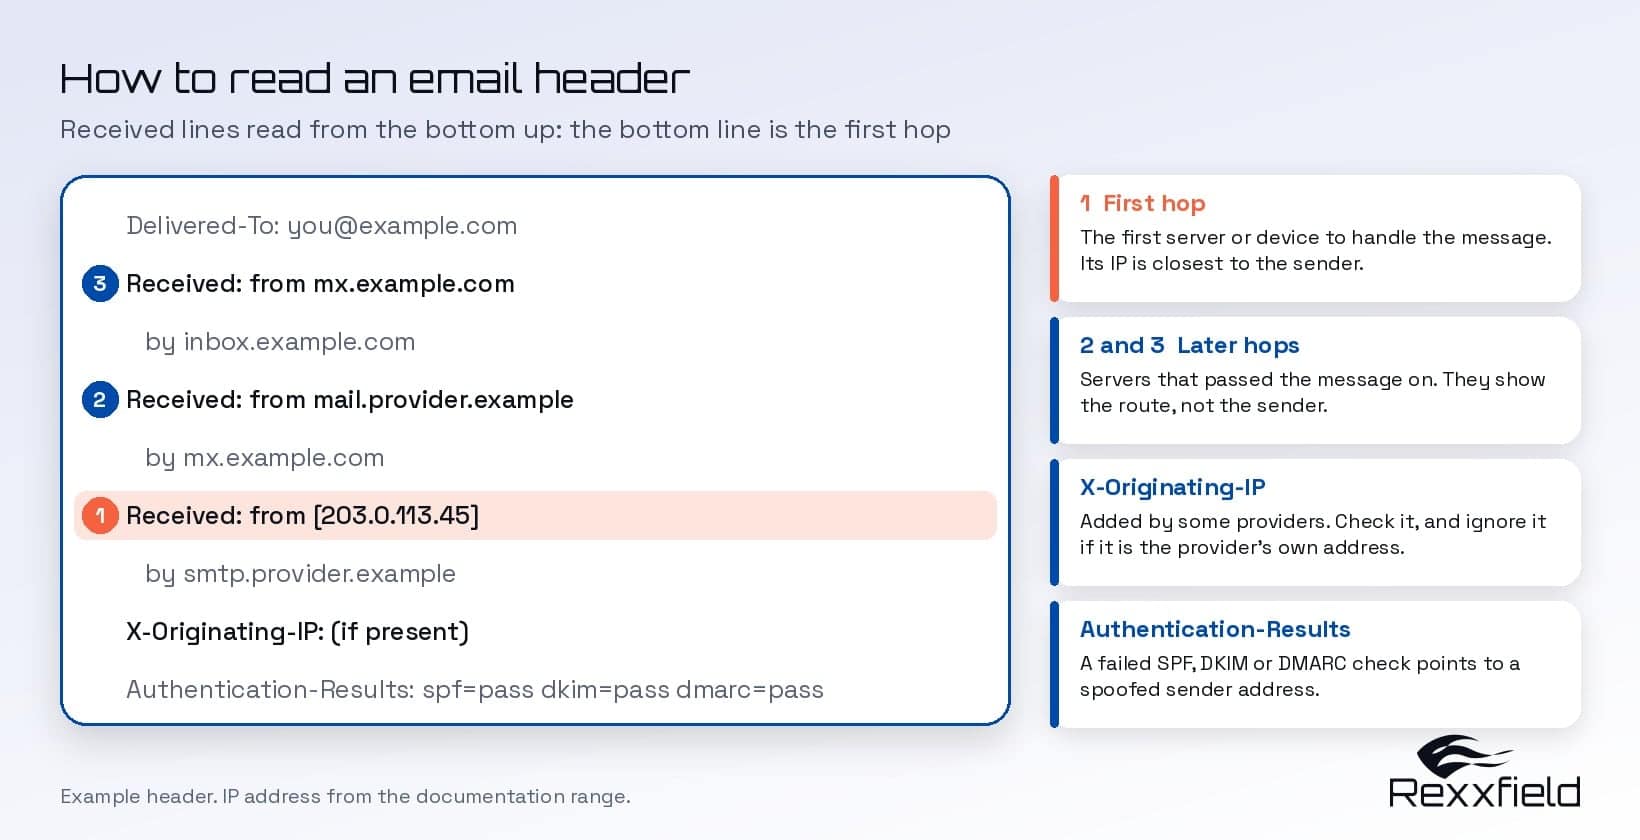
Read the Received lines from the bottom up. The bottom line records the first server that handled the message, and the IP address beside it is the closest you will get to the sender. Also look for a line called X-Originating-IP, which some providers add. If every address you find belongs to the provider, such as Google or Microsoft, the header holds no sender IP. An email header analyzer will lay the hops out in order if you paste the full header into it.
Why Gmail and Proton Mail often show no sender IP
Most harassing and fraudulent email we see comes from Gmail and Proton Mail accounts, and both usually hide the sender’s address. Gmail often shows only a Google address. Sometimes, when the sender used a phone or a desktop program such as Outlook, the sender’s own address appears in the header, so it is always worth checking. Proton Mail leaves the sender’s IP address out of its headers, which is why header tracing fails on Proton accounts. Our guide on whether Proton Mail can be traced covers the routes that do work, and our guide on whether Gmail can be traced explains what a Gmail header shows and what Google keeps.
Fake email sender or spoofed email?
A fake email sender usually works from a real mailbox opened under a false name. Someone controls it and signs in to it, so it leaves sign-in records that an investigation can follow.
A spoofed email is different: the sender address in the message is forged, and no mailbox with that name may be involved.
Spoofing is how most phishing and business email compromise attacks begin. Receiving mail systems check for it with three published records, SPF, DKIM and DMARC, which let a system verify that a message really came from the domain it claims.
A failed check in the header’s Authentication-Results line points to spoofing. When the sender address is forged there is no account to trace, and the investigation looks at the sending infrastructure instead. See our guide to email spoofing.
Can you find an email’s location?
Only approximately, and only when the header contains the sender’s own IP address. A lookup gives a city or region and an internet provider. That is enough to help rule suspects in or out: if the address resolves to a city your suspect has never visited, that matters. It cannot place the sender at a specific address, and mobile connections often resolve to the carrier’s regional hub rather than the user’s town.
Step 2: Check what you can find yourself
Before you spend money, run a few free checks. They work best when the sender used the address elsewhere or reused a username, and they cost nothing but time.
- Search the full email address in quotes on a search engine. Add the part before the @ as a separate search.
- Search that username on the main social networks and forums. People often reuse the same handle.
- Run a reverse image search on the account’s profile photo. A stolen photo often traces back to its real owner, which shows the account is fake.
- Save what you find with screenshots, dates and links. Do not contact the account or the people you find.
Treat any match as a lead, not proof. A shared username can belong to a different person. If your searches turn up nothing or you want the matches verified, move to Step 4, where an investigator goes much further.
Step 3: Subpoena the email provider
In a legal case, your lawyer can file a civil lawsuit against “John or Jane Doe” and subpoena the email provider for the account’s registration details and sign-in IP addresses. The provider then notifies the account holder, who can challenge the subpoena in court. Under US law an unknown defendant may respond anonymously, so the sender learns you are coming. The process takes at least 30 days and often several months.
Registration phone numbers and recovery emails on fake accounts are usually false, so ask for IP addresses and sign-in logs. Once you have an IP address, a second subpoena to the internet provider names the customer behind it. Each provider has its own process:
- Google is a California company and can contest jurisdiction, which adds delay.
- Proton Mail is a Swiss company. It responds only to valid Swiss legal process, and foreign requests usually go through the MLAT process.
- Yahoo, Microsoft and AOL each publish a legal-process contact.
We have step-by-step guides for serving a subpoena on Google, Yahoo and Microsoft. Rexxfield also prepares the subpoena for your lawyer or for law enforcement, which cuts legal costs and reduces the chance the provider returns incomplete data. Order subpoena preparation (flat fee, $1,000).
Step 4: Use an investigator to identify the fake email sender
Tracing the IP address is one part of an investigation, and often the smallest part. A fake email sender leaves more evidence in the account, the writing, the files and the other accounts tied to it than in a single header. A cyber investigator works through those layers in order and reports how confident each finding is.
Map the account and the person behind it
We start by mapping everything the fake email sender has exposed: usernames, display names, linked profiles, bios, reused photos, posting times, writing style and any details they disclosed by accident. People reuse handles and phrases across platforms. We build a profile of the persona first, and we tie it to a real person only when the evidence supports it.
Run technical checks on the account and the evidence
The email header is one source among several. We also check domains the sender operates, current and historical registration records, and email address patterns. We run reverse image searches on profile photos and review files the sender sent for hidden metadata, such as document authorship or device details. Where the law allows, we check whether the address or username appears in known data breaches. Many platforms strip metadata from uploads, so we note what each source can and cannot show.
Score the possible suspects
If your case points to real people, we compare each one against the evidence: location, timeline, motive, writing style and public records. Each candidate gets a confidence rating, and we record the evidence that argues against them as well as for them. Sometimes the honest finding is that several people fit and none fits cleanly. We say so, because a named suspect without evidence puts you at risk in court.
Go to the institutions that hold the records
Some of the records you need are not on the internet. Property filings, court records, business registrations and professional licenses are public, and an investigator knows where to find them. Other records sit with an institution, such as a police department, a school or an employer. We identify who holds the record and the lawful route to request it, which your attorney or law enforcement can then use.
Use controlled contact when passive research stalls
When open sources run out, an investigator can use controlled, lawful contact with the account to capture technical details of the person using it, such as an IP address and device information. We plan this carefully with your attorney, because the legal and safety rules matter as much as the technique. If you have a suspect, we compare those details with the suspect’s. A match is evidence the two are the same person.
A captured IP address also settles jurisdiction. An address in Texas, for example, puts the case in a Texas court and removes the delay of going through Google first.
Prepare legal process for your attorney
When the data you need sits with a provider, we prepare the factual basis, the list of records to request and the wording of the subpoena or preservation letter for your attorney. A well-prepared request reduces the chance the provider returns incomplete data.
Deliver evidence you can use
Our reports document each finding with its source, and our affidavits and testimony support a request for a protective order or injunction. We keep the evidence in a form your attorney and the court can rely on. Read how we identified a Proton Mail sender in this case study.
What an investigator cannot promise
No investigator can guarantee a name. Some cases reach a point where only the email provider holds the record that identifies the sender. In that case we tell you plainly, explain why, and recommend the cheapest real path forward, which is usually a subpoena prepared by your attorney.
Our cyber investigators handle this work from first review to final report. Contact us to talk through your situation.
Or see all of our cyber investigation services.
What to do while you decide
If a fake email sender is harassing you, keep every email with its full header, and take screenshots of the account and the messages. Do not reply in anger, because a reaction usually escalates harassment. Do not click links in the messages. Report threats and extortion to the police. If you are weighing a lawsuit, read how to identify an anonymous online harasser before filing one.
How to Identify an Anonymous Online Harasser Before Filing a Lawsuit
Frequently asked questions
Can an anonymous email be traced to a real person?
Yes, but rarely from the email alone. The header may show an IP address, and a subpoena to the internet provider can name the customer. An investigation can also tie the account to a person through other evidence.
Can the police trace an anonymous email?
Police can obtain records from an email provider through legal process. Whether they will depends on the severity of the messages and their resources, and a well-prepared request improves the odds.
Can you find who owns an email address?
Searching the address and reading the header cost nothing, but they identify the owner only when that person left a public trail. For a fake or anonymous account, an investigation or a subpoena is usually needed.
Can a private investigator trace an email?
Yes, and tracing the IP address is only part of the work. A cyber investigator can analyze the header, map the account across platforms, check domains and file metadata, compare suspects against the evidence, and prepare legal process for your attorney. Rexxfield’s cyber investigators specialize in identifying the person behind anonymous email accounts.
What can a cyber investigator do besides trace an IP address?
An investigator can connect the account to other accounts and real people through open-source research, review technical evidence such as domains and file metadata, request records from the institutions that hold them, and use controlled contact with the account when other methods stall. The findings go into a report your attorney can use.
Contact our cyber investigators to discuss your situation.
Rexxfield is a cyber-investigations firm, not a law firm. This article is general information, not legal advice.